The PurpleOps database monitors group activity to identify trends in Healthcare sector targeting across global networks. Ransomware groups compromised 301 victims in 90 days within the Healthcare sector. The data collection captures incidents between 2026-08-05 and 2026-11-02. The total represents a +61% increase compared to the prior window. Tracking indicates The Gentlemen: 29 victims accounted for the highest single group volume in this specific timeframe.
How have Healthcare victim counts trended over six months?
The PurpleOps database measures Healthcare ransomware volumes over consecutive periods to establish sector activity trends. Security teams rely on this windowed approach to compare current attack volumes against historical data. The prior window captures the incidents recorded from 2026-05-07 to 2026-08-04. During this preceding time frame, groups compromised 187 victims in the Healthcare sector. The difference between the volume in the prior reporting block and the volume in the current reporting block drives the observed percentage increase across the sector. This comparison helps define the trajectory of group operations.
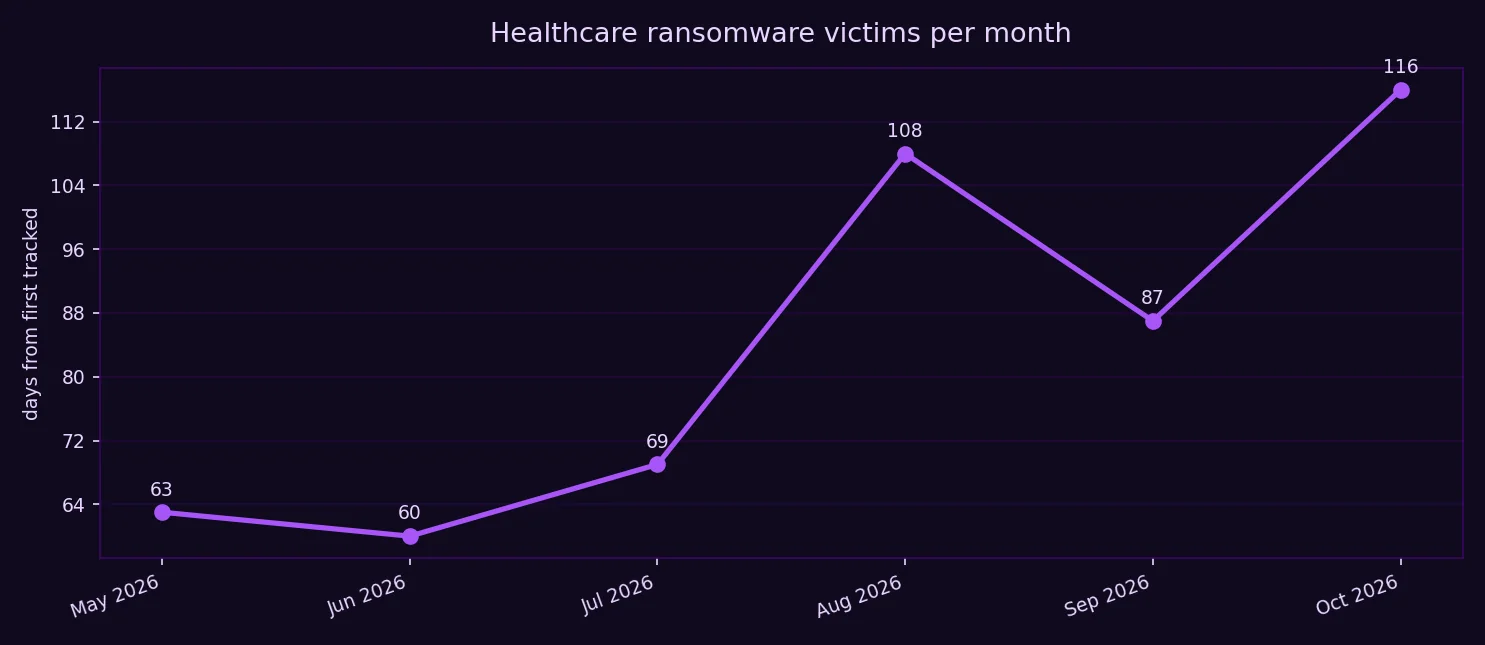
Monthly victim volumes over the last 6 months define the distribution of these attacks. Analysts review month-by-month records to track variations in ransomware deployment. The PurpleOps database recorded 63 victims in May 2026. The following month, groups compromised 60 victims in Jun 2026. During Jul 2026, the database tracked 69 victims. Activity increased in Aug 2026, and groups compromised 108 victims. In Sep 2026, the database recorded 87 victims. The highest volume over the 6-month period occurred in Oct 2026, when groups compromised 116 victims. The records reflect consistent variations in ransomware deployment across the sector.
Which groups target Healthcare?
The PurpleOps database attributes the attacks in the current window to 67 distinct groups. Analysts monitor these specific groups to determine attribution and track variations in attack volume. A subset of the top 5 groups accounts for specific portions of the sector activity. The data shows clear differences in volume between the groups with the highest volumes and the remaining groups operating in the same space.
The Gentlemen recorded the highest volume among the groups in the current window. DireWolf recorded 17 victims, placing it second among the tracked groups in this dataset. Booba recorded 16 victims in the Healthcare sector. INC Ransom recorded 14 victims. We track this group in our analysis of SonicWall CVE-2026-15409 Exploited by Inc Ransomware. Krybit recorded 13 victims.
The remaining groups within the subset of distinct groups fall into a separate category. These other groups compromised 212 victims. This volume accounts for the remainder of the total victims recorded in the current window. Activity extends beyond the groups with the highest volumes. Analysts review this distribution to track the broader landscape of groups targeting the sector.
Which countries see the most Healthcare victims?
Ransomware groups compromised organizations in 45 countries during the current window. The database clusters geographic data to determine which nations face the highest volume of sector attacks. Analysts review this geographic distribution to map the reach of ransomware campaigns. A subset of the top 5 countries accounts for the highest geographic volumes in the dataset.
The United States recorded 186 victims in the Healthcare sector. Canada recorded 10 victims, the second highest volume among the tracked nations. Brazil recorded 8 victims. Australia recorded 7 victims. Switzerland recorded 6 victims. These records map directly to the locations of the compromised networks.
The remaining nations fall into the other countries category. These other countries recorded 84 victims. The geographic data demonstrates that while attacks occur globally, specific nations record higher concentrations of ransomware incidents. This geographic distribution confirms the total volume of compromised organizations recorded across the sector.
Security teams track group infrastructure and geographic targeting using JINX. Analysts use BUGSY to attribute attacks to the distinct groups identified in the dataset and map out sector targeting. These products support the continuous monitoring of ransomware volumes. For access to the full dataset covering the Healthcare sector, visit our ransomware tracking portal.