Update log: Updated 2026-11-03: refreshed platform data.
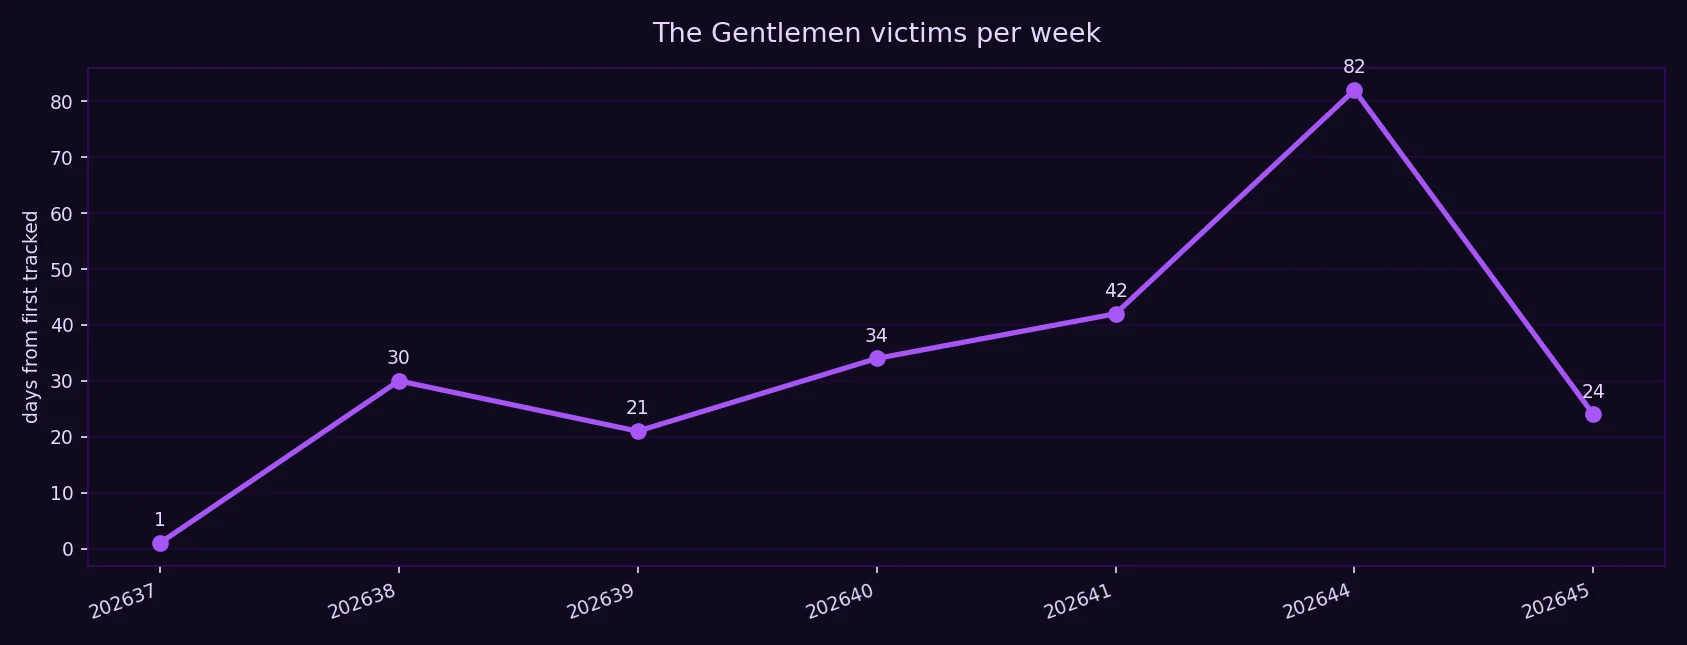
Between 2026-10-27 and 2026-11-03, PurpleOps recorded 106 victims claimed by The Gentlemen. The 7 days of activity demonstrate an aggressive push by The Gentlemen during the monitored window.
Who is The Gentlemen and how active is it?
PurpleOps data identifies The Gentlemen as a highly active ransomware threat. PurpleOps analysts track The Gentlemen executing attacks well above standard operational levels. The Gentlemen maintained a prior 4-week weekly average of 52.7 compromised organizations. Surpassing this baseline demonstrates an expansion in activity and operational capacity. The Gentlemen structures campaigns to maximize pressure on targets. By attacking numerous organizations simultaneously, The Gentlemen attempts to overwhelm security responses and force rapid payments. The sustained volume of attacks requires an established infrastructure to process victims, negotiate ransom demands, and distribute stolen files. Managing this scale of operations involves coordination across the entire network. PurpleOps continues to monitor The Gentlemen to identify shifts in deployment cycles and track fluctuations in attack frequency.
Which sectors and countries does it hit?
The Gentlemen executes campaigns against a broad range of targets. PurpleOps data confirms The Gentlemen impacted organizations across 39 countries. Impacting networks globally shows The Gentlemen maintains an opportunistic targeting strategy across international boundaries. The Gentlemen hits networks wherever vulnerabilities exist.
The Gentlemen attacks critical industries to maximize operational disruption. Manufacturing emerged as the top sector, accounting for 13 recorded incidents. Factory administrators face downtime costs during ransomware attacks. PurpleOps analysts observe that Manufacturing Sees 477 Victims in 90 Days provides data on the persistent threats facing the industrial base.
The Gentlemen claimed 12 organizations in the Technology / Software sector. The Gentlemen also targeted the Healthcare industry, posting 12 victims. The threat against hospitals matches the pattern where 301 Victims in 90 Days Hit the Healthcare Sector, requiring defenders to prioritize network segmentation.
Further PurpleOps tracking identifies 10 victims claimed by The Gentlemen in Construction & Engineering. Attacks against construction firms disrupt project timelines and expose proprietary architectural data. Education accounted for 9 victims. Claiming targets from Manufacturing to Education confirms The Gentlemen does not restrict targets to specific industries.
How does The Gentlemen operate?
PurpleOps actor profiles detail the specific mechanisms The Gentlemen uses to conduct network intrusions and extort victims. The Gentlemen prepares operations by using T1585 Establish Accounts. The Gentlemen creates profiles to conduct RaaS Affiliate Recruitment. Building a broad attack network allows The Gentlemen to scale attacks and target various sectors concurrently.
The Gentlemen communicates with the public and announces victims using T1102 Web Service. PurpleOps analysts observe The Gentlemen relying on Telegram for Victim Announcements. The platform provides a decentralized method to publish claims, leak data fragments, and pressure organizations into paying the ransom. Using public channels forces victims to respond to public relations crises alongside the technical incident.
Once inside a network, The Gentlemen steals sensitive files using T1567 Exfiltration to Cloud Storage or C2. Moving data to external servers provides The Gentlemen an advantage for extortion. The Gentlemen threatens to release internal documents, customer records, and financial statements. After securing the stolen files, The Gentlemen executes T1486 Data Encrypted for Impact. The Gentlemen locks critical databases, servers, and workstations to halt business operations completely.
In specific instances, PurpleOps tracking shows The Gentlemen deploys T1485 Data Destruction. Erasing files and rendering systems unrecoverable serves to punish organizations that refuse to pay or attempt to restore from backups. Wiping the disks removes any chance of native system recovery.
How do I detect and contain it?
Security practitioners defending against The Gentlemen must implement precise monitoring for specific MITRE ATT&CK techniques. Identifying The Gentlemen early requires tracking the infrastructure used to organize campaigns. Defenders should scan access broker forums and platforms for T1585 Establish Accounts activity to track RaaS Affiliate Recruitment by The Gentlemen. Security teams must also monitor network perimeters to block connections related to T1102 Web Service. Denying outbound access to Telegram prevents compromised endpoints from communicating with The Gentlemen and stops internal users from accessing victim announcements on corporate devices.
To protect proprietary data, organizations require strict controls against T1567 Exfiltration to Cloud Storage or C2. Security operations centers must configure firewalls and proxy servers to alert on anomalous outbound data transfers. Defenders should restrict access to unapproved cloud storage providers to contain data theft attempts originating from compromised servers.
Containing the final stages of an attack requires aggressive endpoint defense against The Gentlemen. Security teams must deploy behavioral rules to identify T1486 Data Encrypted for Impact. Defenders need endpoint detection platforms configured to kill processes attempting to mass-modify files. Organizations must also monitor administrative shares and critical directories to detect T1485 Data Destruction. Blocking unauthorized disk wiping commands prevents The Gentlemen from permanently destroying corporate data before ransom negotiations begin.
Security teams require continuous intelligence to defend against The Gentlemen. Tracking the technical mechanisms and victim distribution helps organizations prioritize security investments. Defenders can deploy JINX to identify active network threats and use BUGSY to test detection rules against known ransomware behaviors. Organizations needing access to comprehensive threat intelligence data can review the PurpleOps dashboard by visiting https://purple-ops.io/solutions/ransomware-tracking.